Microsoft has pointed out under KB5036210 that Windows Updates from February 13, 2024 and later will install the Windows UEFI CA 2023 certificate on the UEFI Secure Boot Allowed Signature Database (DB). This allows upcoming bootloader updates to be installed directly via Windows Update.
As Microsoft writes, this is important “As the existing certificate expires and switching to the new certificate is the first step in preparing devices to work with upcoming bootloader updates that will be encrypted with the new certificate.”
Please note that some devices may experience database compatibility issues. For example, ARM64-based devices are currently excluded. Here Microsoft works with the OEM manufacturers. Therefore, the updates are currently not delivered automatically.
In companies, the change should therefore first be tested on a selected device before it is applied to all devices. In order for the certificates to be installed via Windows Update, a change must be made in the registry.
- Windows key + R enter regedit, open it and switch to this path
HKEY_LOCAL_MACHINESYSTEMCurrentControlSetControlSecureBoot- Then double-click in the right part of the window
AvailableUpdatesand change the value to 40.
This can be set up using PowerShell
- The February 2024 security update must be installed.
- Start PowerShell (administrator) and enter this command
Set-ItemProperty -Path "HKLM:SYSTEMCurrentControlSetControlSecureBoot" -Name "AvailableUpdates" -Value 0x40
- Start a scheduled task:
Start-ScheduledTask -TaskName "MicrosoftWindowsPISecure-Boot-Update"
- Restart the PC twice
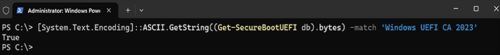
- Now enter the following command in PowerShell (Admin):
[System.Text.Encoding]::ASCII.GetString((Get-SecureBootUEFI db).bytes) -match ‘Windows UEFI CA 2023’
- PowerShell should now be on True output as a result.