Owners of Anycubic 3D printers are reporting in droves that someone hacked their devices and left a note warning them that the printers are vulnerable to attacks (1, 2, 3). An unknown well-wisher recommends that users disconnect their devices from the Internet.
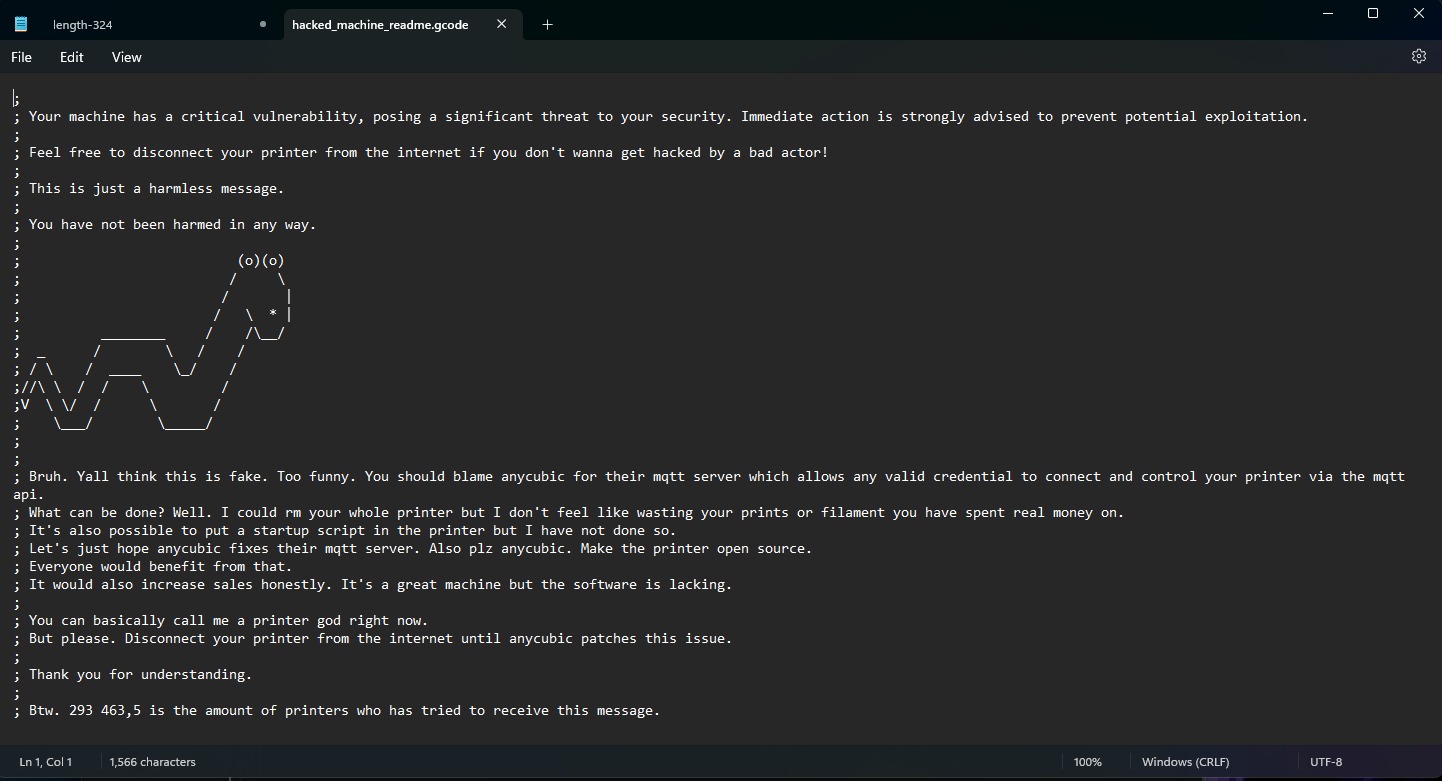
An unknown person placed the hacked_machine_readme.gcode file on hacked devices, warning users about a certain critical vulnerability. Allegedly, this bug allows attackers to control any Anycubic 3D printer using the MQTT service API.
Also in his message, the anonymous author asks the Anycubic company to open the source code of 3D printers, since the software currently “has shortcomings.”
“Your device contains a critical vulnerability that poses a significant threat to your security. It is strongly recommended that immediate action be taken to prevent potential exploitation. You can disconnect the printer from the Internet if you do not want it to be hacked by intruders. It's just a harmless message. No harm came to you, the message reads. – Blame anycubic for their mqtt server, which allows you to use any valid credentials to connect and control your printer via the matt API. Let's hope anycubic fixes their mqtt server.”
According to the message from an unknown hacker, 2,934,635 devices downloaded this message through the vulnerable API.
Anycubic representatives are already collecting information from affected customers (APP account names, CN codes, device logs and gcode files) on social networks in order to “diagnose the problem.”
The Anycubic app stopped working just hours after users began posting online complaining that their 3D printers had been hacked. According to the publication TechCrunchusers currently trying to log in are seeing “Network unavailable” error messages.
Although Anycubic has not yet released an official statement about the situation, on a forum dedicated to 3D printing, affected users are sharing anonymous post, which was published last Tuesday. The post warned of two critical vulnerabilities affecting the company's products.
“We tried to contact Anycubic regarding two critical vulnerabilities we discovered, one of which could be catastrophic if found by attackers. Despite our efforts over the past two months, we have not received a single response to our three letters. These vulnerabilities are very serious, and we have spent a lot of time and effort to eliminate them,” the post read. “As such, we are preparing to make the details of these vulnerabilities public along with our repository and tools.”