Today we’ll start with the typical (and not so typical) AS-REP Roasting and Kerberoasting attacks. Then we’ll dig into the LDAP database and find a non-obvious path forward. When gaining access to the host, we use the RemotePotato technique, and to increase privileges, we use the S4U2proxy technique.
Our goal is to obtain superuser rights on the Rebound machine from the training site Hack The Box. Its difficulty level is “insane.”
warning
It is recommended to connect to machines with HTB only via VPN. Do not do this from computers that contain data that is important to you, as you will end up on a shared network with other participants.
Intelligence service
Port scanning
Add the machine's IP address to /:
И запускаем сканирование портов.
Справка: сканирование портов
Сканирование портов — стандартный первый шаг при любой атаке. Он позволяет атакующему узнать, какие службы на хосте принимают соединение. На основе этой информации выбирается следующий шаг к получению точки входа.
Наиболее известный инструмент для сканирования — это Nmap. Улучшить результаты его работы ты можешь при помощи следующего скрипта:
#!/bin/bash
ports=$(nmap -p- --min-rate=500 $1 | grep ^(0-9) | cut -d '/' -f 1 | tr 'n' ',' | sed s/,$//)
nmap -p$ports -A $1
It works in two stages. The first one performs a regular quick scan, the second one performs a more thorough scan using the available scripts (option -A).
The scanner found many open ports, which is typical for Windows servers:
- 53 - DNS;
- 88 - Kerberos;
- 135 - Remote Procedure Call Service (Microsoft RPC). Used for controller-controller and controller-client interaction operations;
- 139 - NetBIOS session service, NetLogon;
- 389 - LDAP;
- 445 - SMB;
- 464 - Kerberos password change service;
- 593 (HTTP-RPC-EPMAP) - used in DCOM and Exchange services;
- 636 - LDAP with SSL or TLS encryption;
- 3268 (LDAP) - to access the Global Catalog from the client to the controller;
- 5985 - WinRM remote management service.
First of all, we check whether anonymous login is possible and display a list of shared directories. To do this we use the utility CrackMapExecwhich will be useful to us more than once during our passage.
crackmapexec smb rebound.htb -u guest -p '' --shares
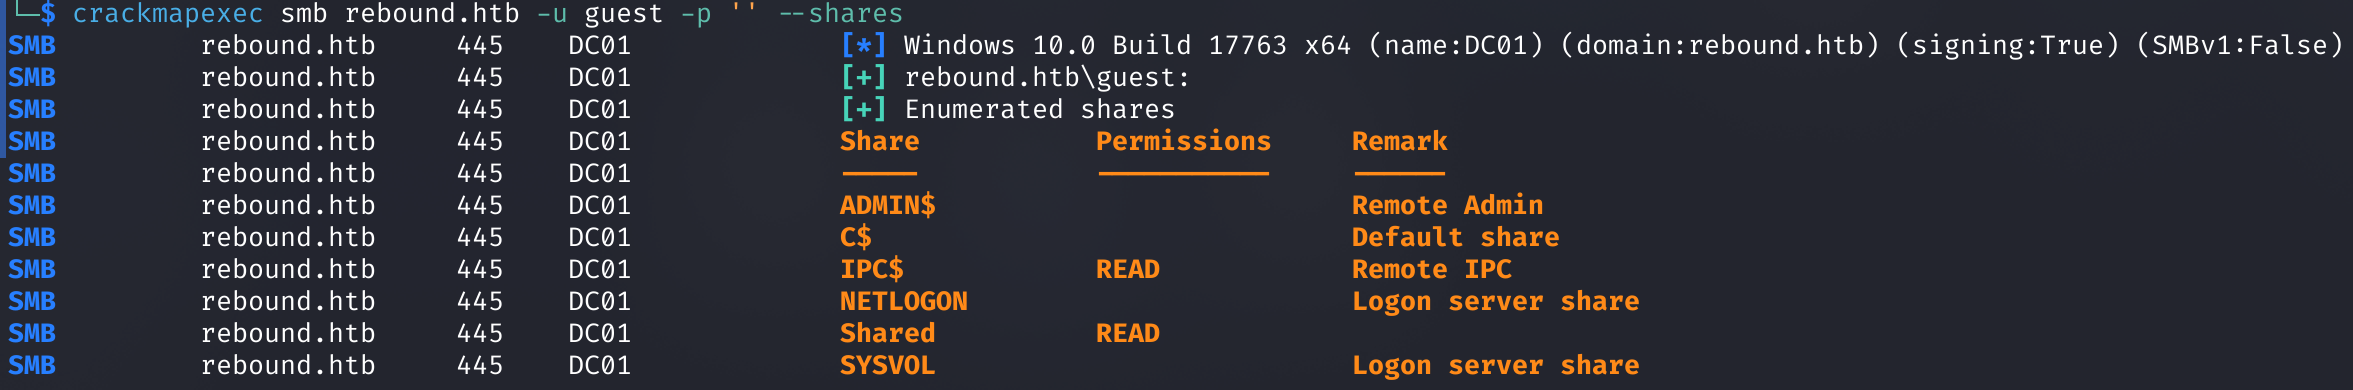
We see a non-standard directory Shared. You can connect and view the content using the script from the set impacket.
impacket-smbclient guest@rebound.htb
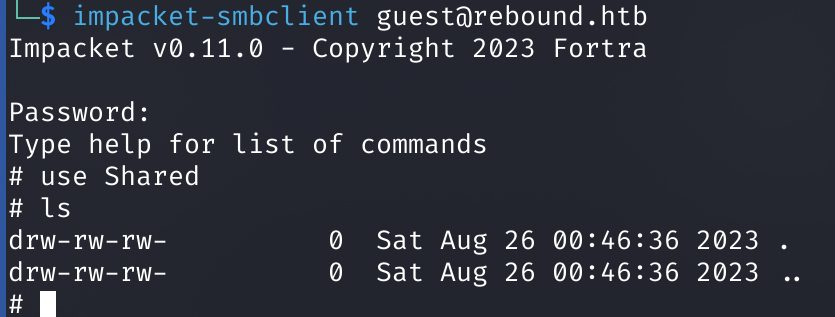
But the catalog turned out to be empty, so we move on to other techniques.
Point of entry
Since anonymous authentication is available on the SMB resource, you can drill through the RID and get group names and user names.
crackmapexec smb rebound.htb -u guest -p '' --rid-brute 10000
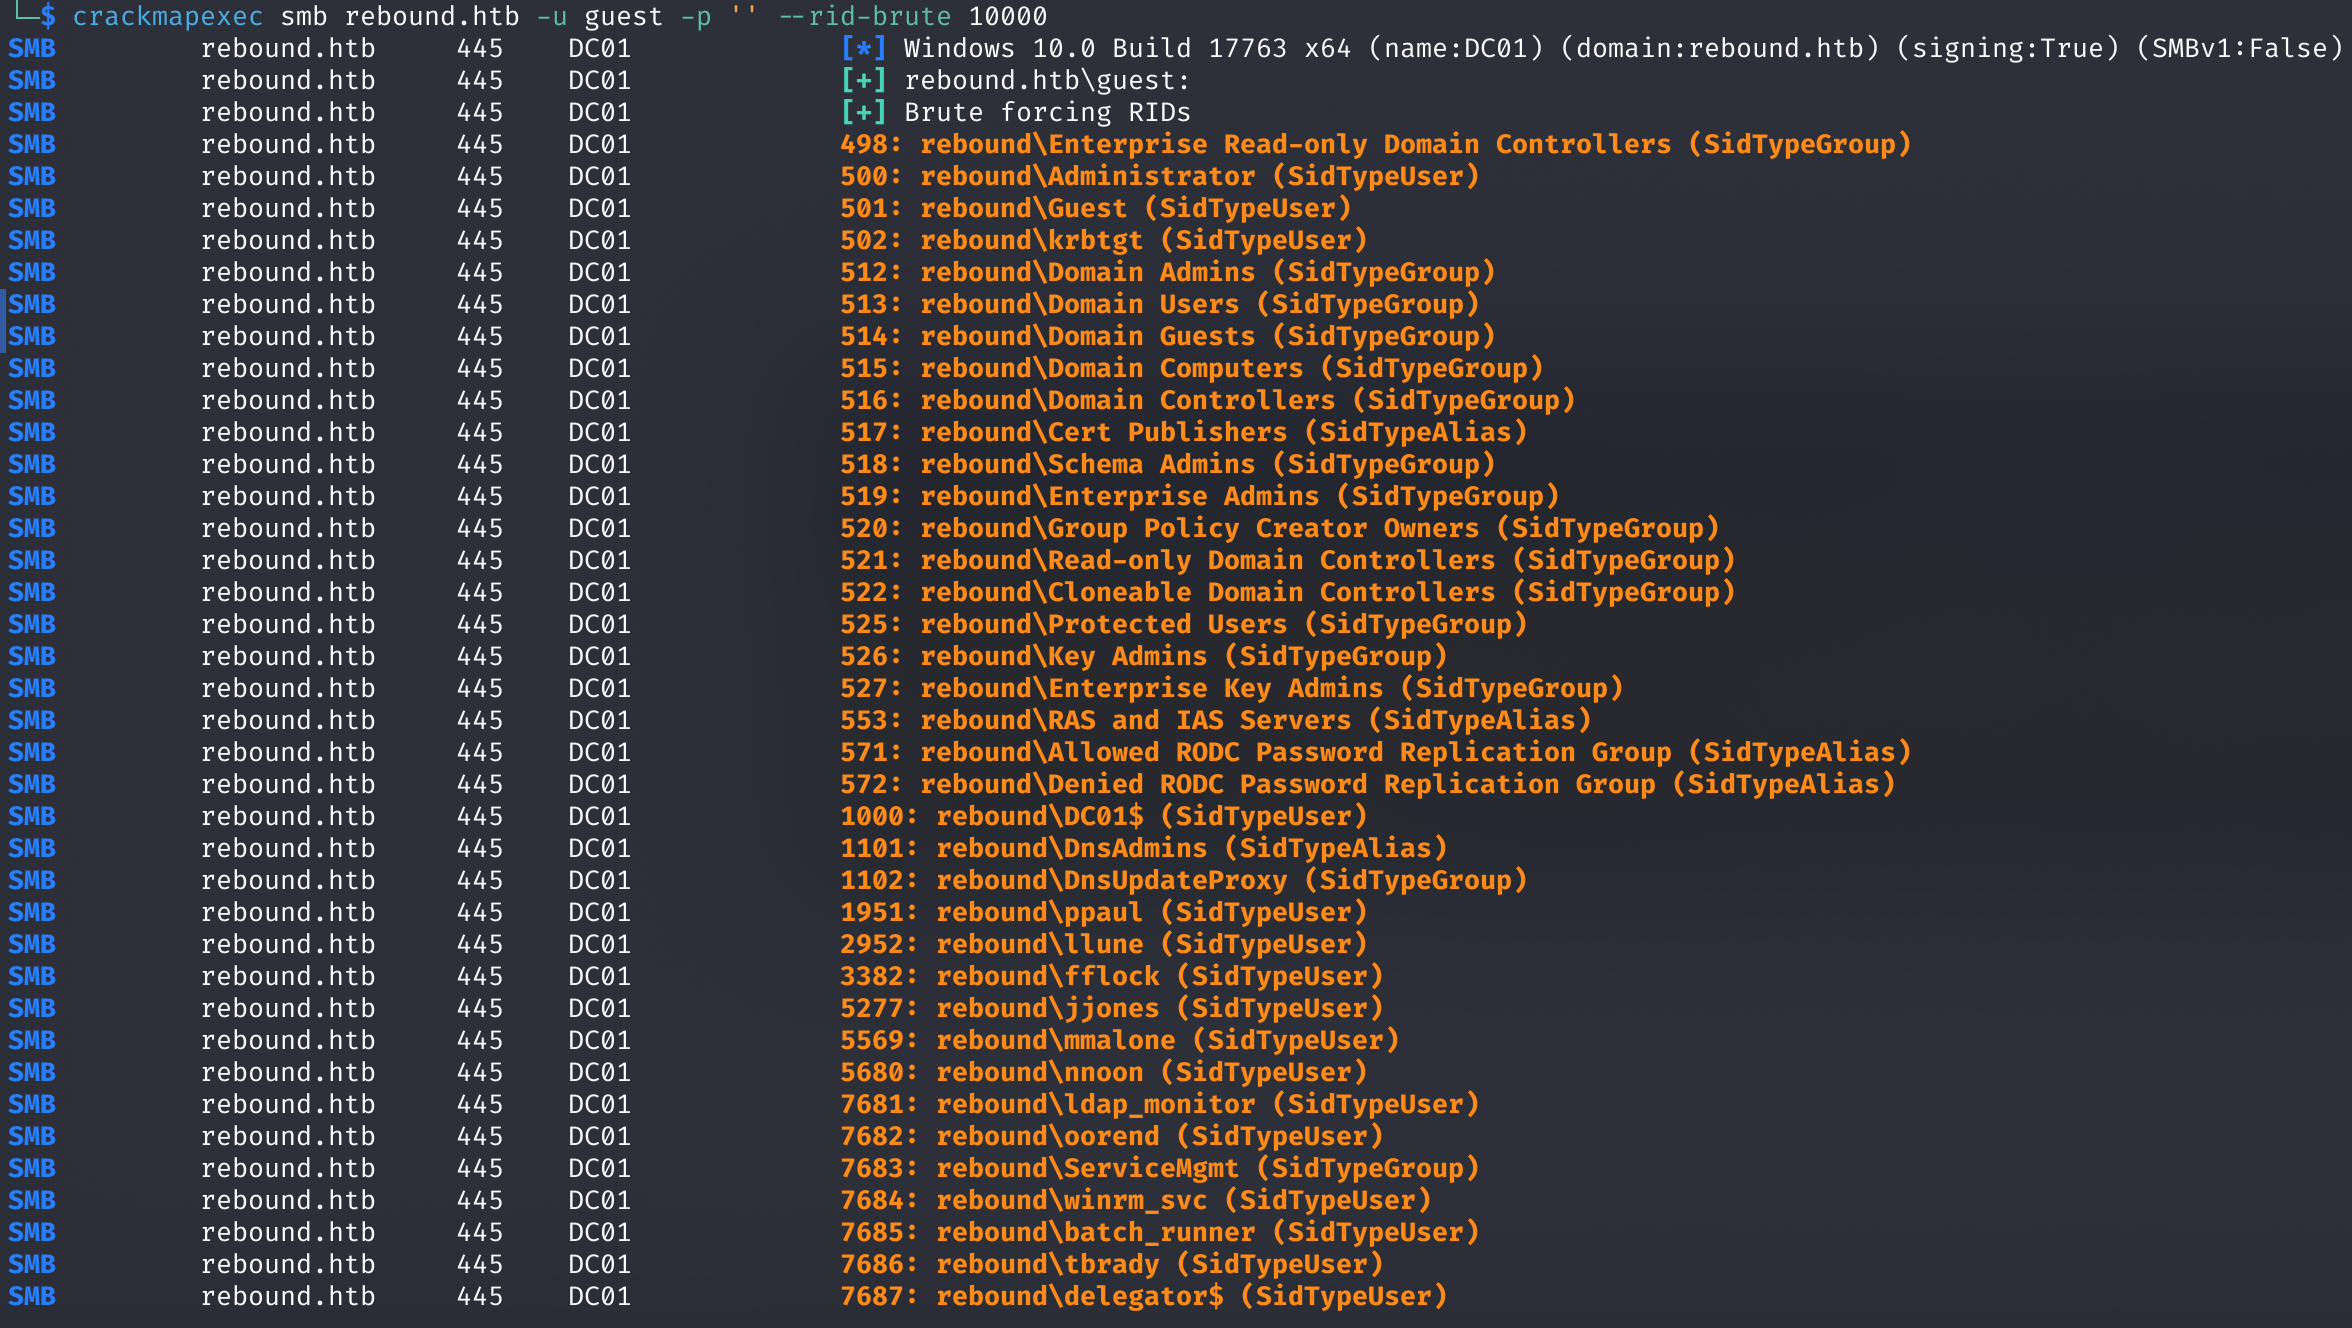
Now that we have usernames, we can guess popular passwords and test AS-REP Roasting.
AS-REP Roasting
The point of the AS-REP Roasting attack is that we send an anonymous request to the authentication server to provide a specific user with access to some service. To which the server has three different responses:
- provides a ticket from where we will get the hash;
- replies that this user does not have the flag set
PreauthNotRequired; - says that such user is not in the Kerberos database.