Stamus Networks Company published release of a specialized distribution kit SELKS 10, designed to deploy systems for detecting and preventing network intrusions, as well as organizing responses to identified threats and monitoring network security. Users are provided with a complete network security management solution that can be used immediately after downloading. The distribution supports working in Live mode and running in virtualization environments or containers. Project developments spread licensed under GPLv3. Two iso images have been generated for downloading: with the Xfce graphical environment (3.5 GB) and running in console mode (2.7 GB).
The distribution is built on the Debian package base and uses the open Suricata attack detection system. Data coming from various sources is processed using the platform Logstash and stored in ElasticSearch storage. To track the current status and identified incidents, a web interface is proposed, implemented on top of the interface Kibana. A web interface is used to manage rules and visualize the activity associated with them. Stamus CE. It also includes a system for capturing, storing and indexing network packets Arkime, an interface for assessing events that have occurred EveBox and data analyzer CyberChef.
Basic improvements:
- Additional features from the parallel developed commercial platform SSP (Stamus Security Platform) have been transferred to the user interface. Work has been done to simplify the web interface and bring together information about detecting threats, searching for suspicious activity and analyzing evidence.
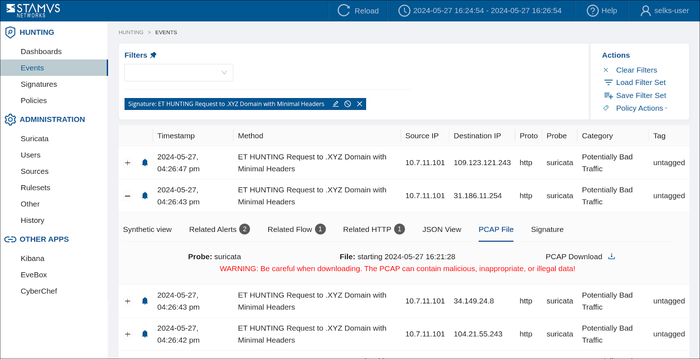
- Added the ability to selectively capture packets associated with detected events and export them from the interface for analyzing suspicious activity in PCAP format. Exported dumps contain complete data about the network session associated with the identified threat. The dump can be used to analyze the incident both in SELKS itself and in third-party tools such as Wireshark.
- The Arkime system for capturing, storing and indexing network packets has been updated to version 5.0, which now includes support for searching information simultaneously about several objects in open sources (OSINT), the design of the block with detailed information has been changed, a unified configuration subsystem has been activated, and support for traffic fingerprinting methods has been added. JA4 And JA4+ and the ability to import saved PCAP dumps has been implemented.
- Instead of SQLite, PostgreSQL DBMS is used to store data.
- The package base has been updated to Debian 12.
Thanks for reading: